Know what's vulnerable.
Fix it today.
Drop any dependency manifest. Get a full vulnerability report with CVSS scores, fix versions, active-exploit flags, and terminal upgrade commands. Free, open-source, stateless.
Powered by OSV.dev · CISA KEV · FIRST EPSS — all public, all free, all live
Where the data comes from
Every number traces back to one of three authoritative public sources. Click a card to understand what it contributes and why you can trust it.
Why trust the scores?
Security data is only useful if you know its provenance.
CVSS scores come from NVD/OSV, not us
Severity scores are computed by NVD analysts and published in CVE records. OSV surfaces them verbatim. No adjustments. The score you see is the same score your enterprise scanner would show.
KEV is US federal government data
CISA's KEV list is mandatory for all US federal civilian agencies. A KEV flag is not a prediction — it means CISA has confirmed active exploitation in the wild.
EPSS is peer-reviewed ML, not guesswork
FIRST's EPSS model is published in academic papers, updated daily, and trained on observed exploit data. A high score means the model has seen patterns that reliably precede exploitation.
Data is live on every scan
Nothing is cached. Every scan hits OSV, KEV, and EPSS fresh. A CVE disclosed yesterday will appear today with its current EPSS score and KEV status.
Your source code never leaves your machine
Manifest files are parsed entirely in your browser. The server only receives a flat list of package names and versions — never file contents, never source code, never paths. No database. No account. Nothing stored between sessions.
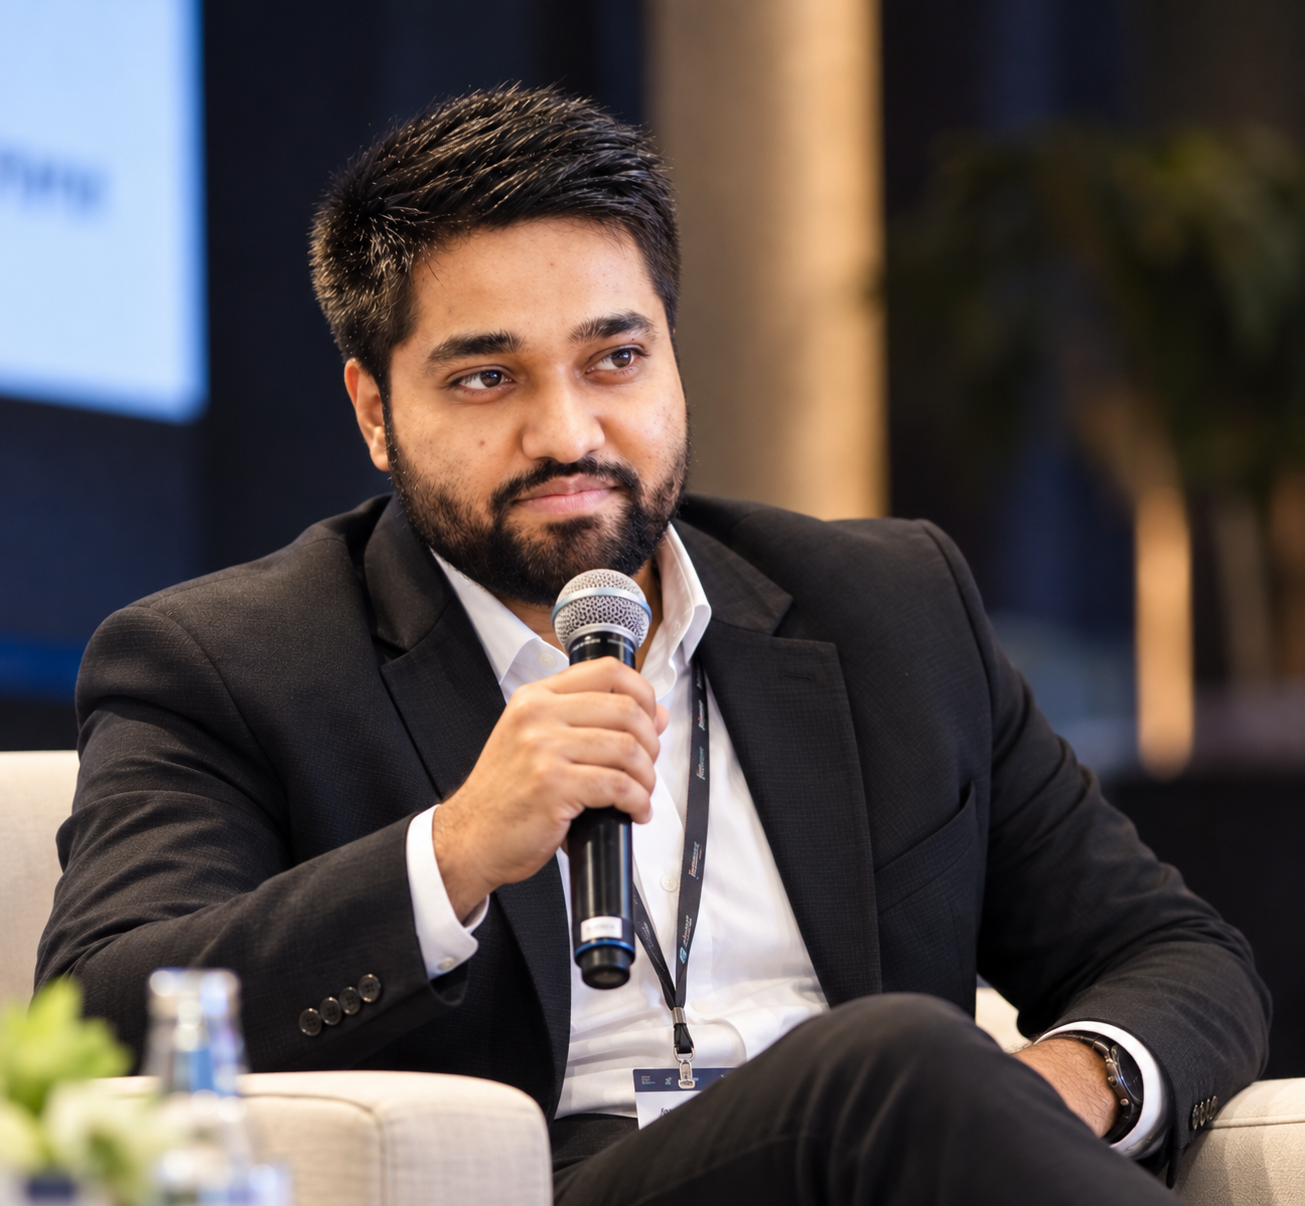
Aditya Ikram Dash
Product Manager · AI Builder · Security Enthusiast
Built this to give every developer — from solo indie hackers to enterprise AppSec teams — instant, free, no-login access to the same vulnerability intelligence commercial tools charge for. Powered entirely by public data.